Skip to content
PT Alpha Citra Siber Indonesia
  • About
  • Solutions & Services
    • Red Team
    • Blue Team
    • Strategic Team
    • Solutions
    • Services
  • Contact
  • News & Event
PT Alpha Citra Siber Indonesia
  • About
  • Solutions & Services
    • Red Team
    • Blue Team
    • Strategic Team
    • Solutions
    • Services
  • Contact
  • News & Event

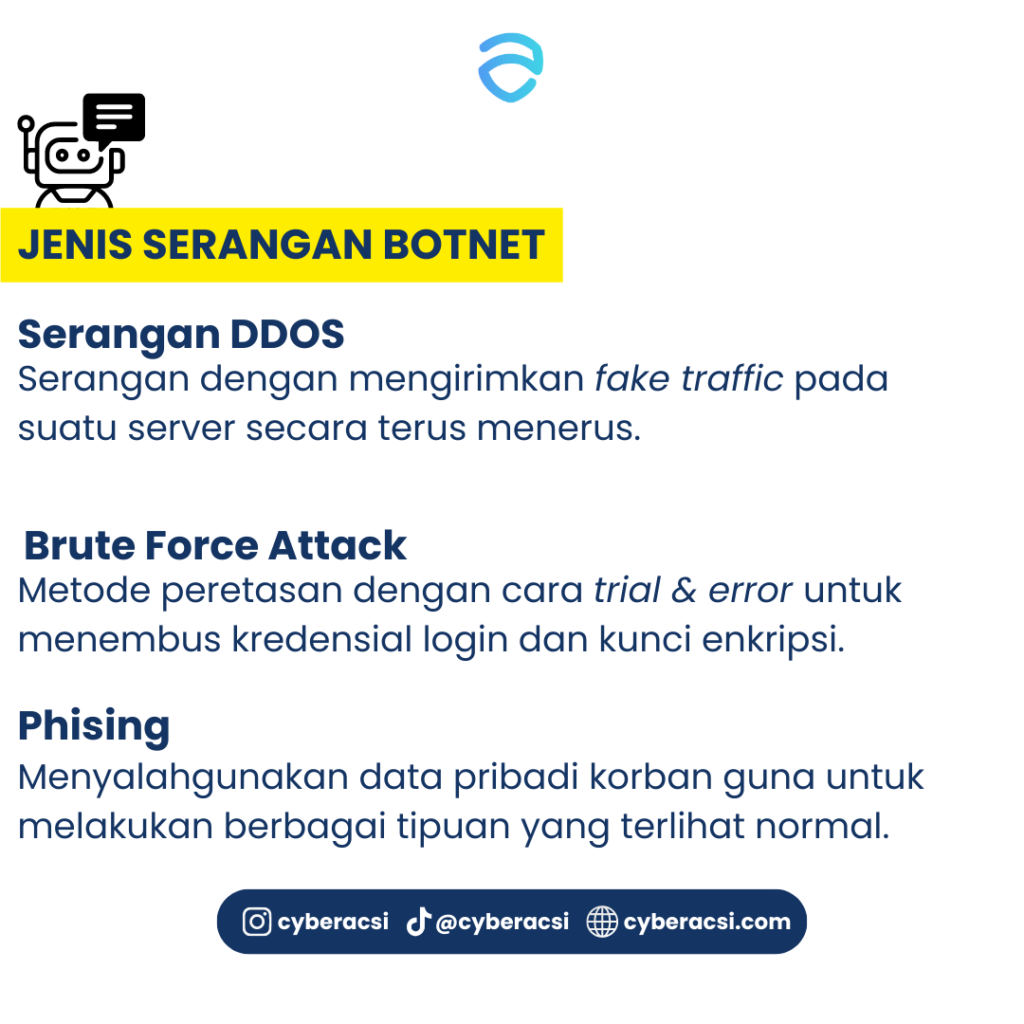
BOTNET = Kumpulan Robot?

/ Uncategorized
← Previous Post
Next Post →


PT Alpha Citra Siber Indonesia

Ebenezer Building, Jl. Setia Budi Selatan No.1, RW.5, Kuningan, Karet,
Kecamatan Setiabudi, Kota Jakarta Selatan,
Daerah Khusus Ibukota Jakarta 12920

Contact Us

Office : 021 5799 4786
Email : info@cyberacsi.com

Copyright © 2026 PT Alpha Citra Siber Indonesia | Powered by PT Alpha Citra Siber Indonesia

SIEM

Security Information and Event Management

Solution Overview

SIEM is a centralized security monitoring solution that collects, correlates, and analyzes security logs from servers, endpoints, network devices, applications, and other IT systems. It helps organizations detect suspicious activities, identify potential threats, and improve security visibility across their IT infrastructure.

!

Pain Points

  • Security logs are scattered across multiple systems, making centralized monitoring difficult.
  • Suspicious activities and cyberattacks may go undetected due to limited visibility.
  • Security teams struggle to correlate events and investigate incidents efficiently.
  • Compliance requirements demand better security logging, monitoring, and reporting.
✓

Benefits / Advantages

  • Centralized visibility into security events across the IT environment.
  • Faster identification and investigation of potential security incidents.
  • Improved threat detection through event correlation and analytics.
  • Enhanced audit readiness and support for regulatory compliance.
Strengthen Your Security with SIEM Contact our team for a personalized consultation.
Contact Us →
mengapa-ancaman-dari-dalam-insider-threat-risiko-terbesar

SIEM

SIEM is a centralized security monitoring solution that collects, correlates, and analyzes security logs from servers, endpoints, network devices, applications, and other IT systems. It helps organizations detect suspicious activities, identify potential threats, and improve security visibility across their IT infrastructure.

Pain points

  • Security logs are scattered across multiple systems, making centralized monitoring difficult.
  • Suspicious activities and cyberattacks may go undetected due to limited visibility.
  • Security teams struggle to correlate events and investigate incidents efficiently.
  • Compliance requirements demand better security logging, monitoring, and reporting.

Benefits

  • Centralized visibility into security events across the IT environment.
  • Faster identification and investigation of potential security incidents.
  • Improved threat detection through event correlation and analytics.
  • Enhanced audit readiness and support for regulatory compliance.